
 Μake us preferred on Google
First, artificial intelligence heralded the Bugmageddon. Now it is triggering an all-hands-on-deck cyber emergency.
The creators of PHP, a technology that powers as much as 70% of the world’s websites, disclosed a critical security issue Wednesday that could be leveraged by hackers to take control of any system running its software. That would allow an attacker to steal information or launch a cyberattack on anyone visiting a hacked website.
Security researchers found the vulnerability using AI. Now web administrators are scrambling to protect themselves from the vulnerability, which cutting-edge AI systems could quickly exploit. Some say they are pre-emptively taking their sites offline.
The issue, dubbed PHP2Shell, represents a class of problems in the way PHP manages a computer’s memory. It can be exploited in many ways, some requiring just a few seconds, by hackers who could use it to run unauthorized software on any unpatched web server.
It is the most severe security issue that PHP has faced in more than a decade, according to Volker Dusch , a security engineer with the nonprofit foundation that manages the PHP project. He likened it to Heartbleed, a similarly widespread vulnerability that forced a global race to protect hundreds of thousands of servers more than a decade ago.
When security patches are released, it marks the starting shot in a race between defenders and hackers. Defenders have to test and install the software patches, while hackers study the patches as a guide to find new vulnerabilities, looking to see what has changed and then devising ways of attacking those areas.
But today’s AI tools can do this work much quicker than any human, potentially making the process more risky, security experts say.
“Some dude on Twitter could take the patches and run AI against it and post some exploit script,” said Thai Duong , the chief executive of Calif, the security company that first discovered the issue. “All hell will break loose.”
The big bug
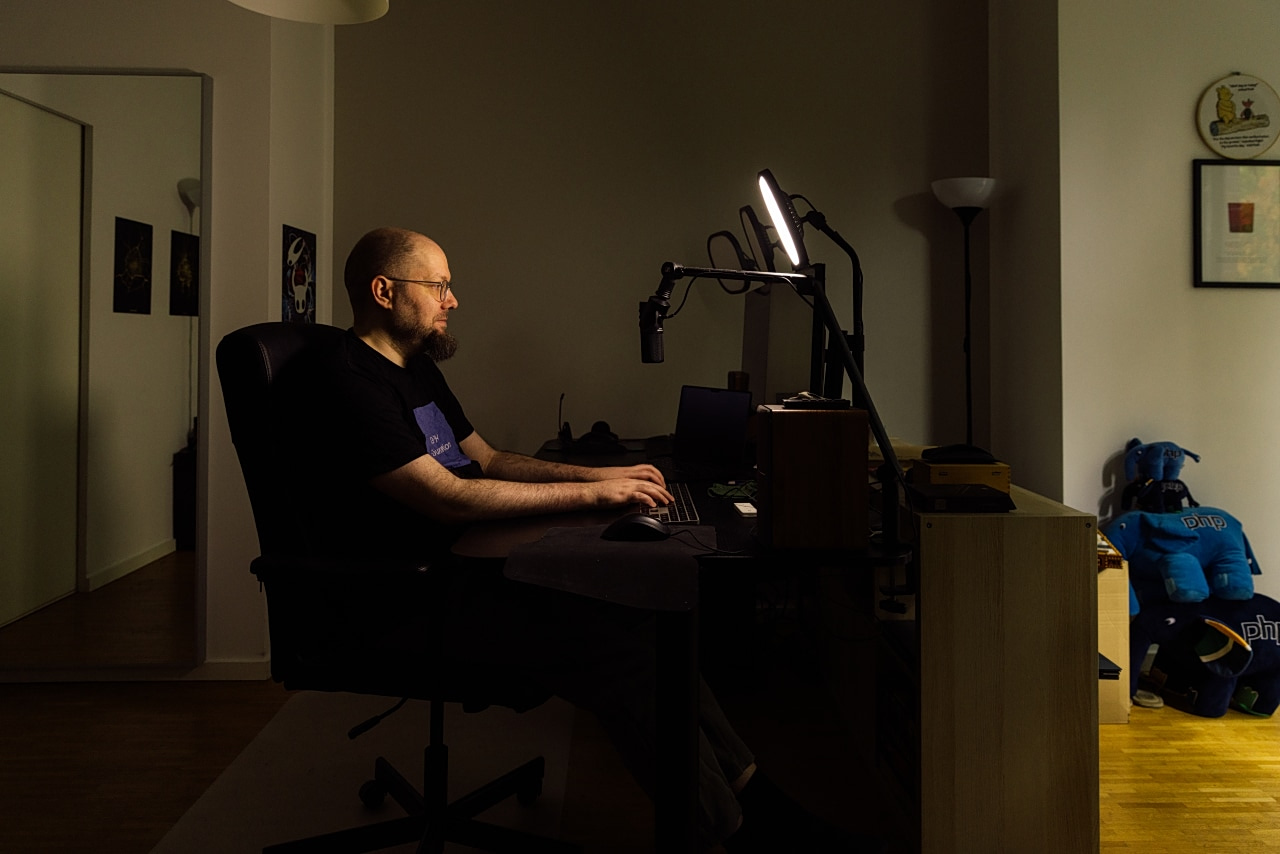
Ryan Austin , a researcher at Calif, uncovered the flaws with help from GPT-5.6 Sol, one of OpenAI’s most advanced models, during an audit of PHP’s source code in August. OpenAI funded that and other audits, part of an effort by AI companies to help open-source projects address software vulnerabilities now being uncovered by artificial intelligence systems.
The class of bugs had been hiding in PHP’s source code for years. A security researcher had flagged it as a problem area decades earlier, but the flaw had been considered too difficult to exploit and was largely forgotten, Duong said.
AI found a way. Austin figured out how to control the code that was running in the computer’s memory with as few as a few dozen requests to a server running PHP. On smaller systems, the hack takes just seconds. On more complex ones, it can take hours.
On Aug. 11, Duong called PHP’s Dusch. “There’s a serious issue here,” he said.
“I had a moment of, ‘Oh God, what are we doing now?’” Dusch said. “‘How do I communicate this?’”
“And then you calm down, you let the adrenaline flow through, and you get to fixing,” he said.
Soon an informal working group had formed among security researchers and software engineers. They collaborated with software distributors and security companies, figuring out ways to patch PHP2Shell and prevent it from being exploited.
Researchers from Google’s Wiz cybersecurity team soon reached out with new exploits, which they had discovered independent of Calif. There were findings from OpenAI’s research team, too.
AI is enabling well-meaning security researchers to find thousands of software bugs, overwhelming projects like PHP with a flood of issues that need patching. But PHP2Shell was viewed as a priority and AI’s proficiency at hacking prompted worries that criminals could exploit PHP2Shell on many websites before they can be patched.
Keeping the secret
PHP2Shell is “the most severe AI vulnerability that was ever found,” and one that was likely too complex to have been discovered without AI, said Ami Luttwak , Wiz’s co-founder.
Duong and the other researchers kept its existence a closely guarded secret while they worked on fixes, for fear that an AI-aided hacker might find and exploit it before they were done.
The patching effort was massive. There are close to 200 files being fixed and developers wrote over 10,000 lines of code during the process.
Eventually, a patch date was set: October 22. Then, the inevitable happened. News of the patch leaked out Tuesday, in a post to Hacker News , just under two days before the patch release.
Dusch’s team decided to rush out the patch. On Tuesday, they warned the world to stand by and expect a critical security update on Wednesday.
It was “a good balance to inform defenders,” Dusch said, “and not give attackers too much time to develop exploits.”